It’s not the attack, but the preparation that makes the difference
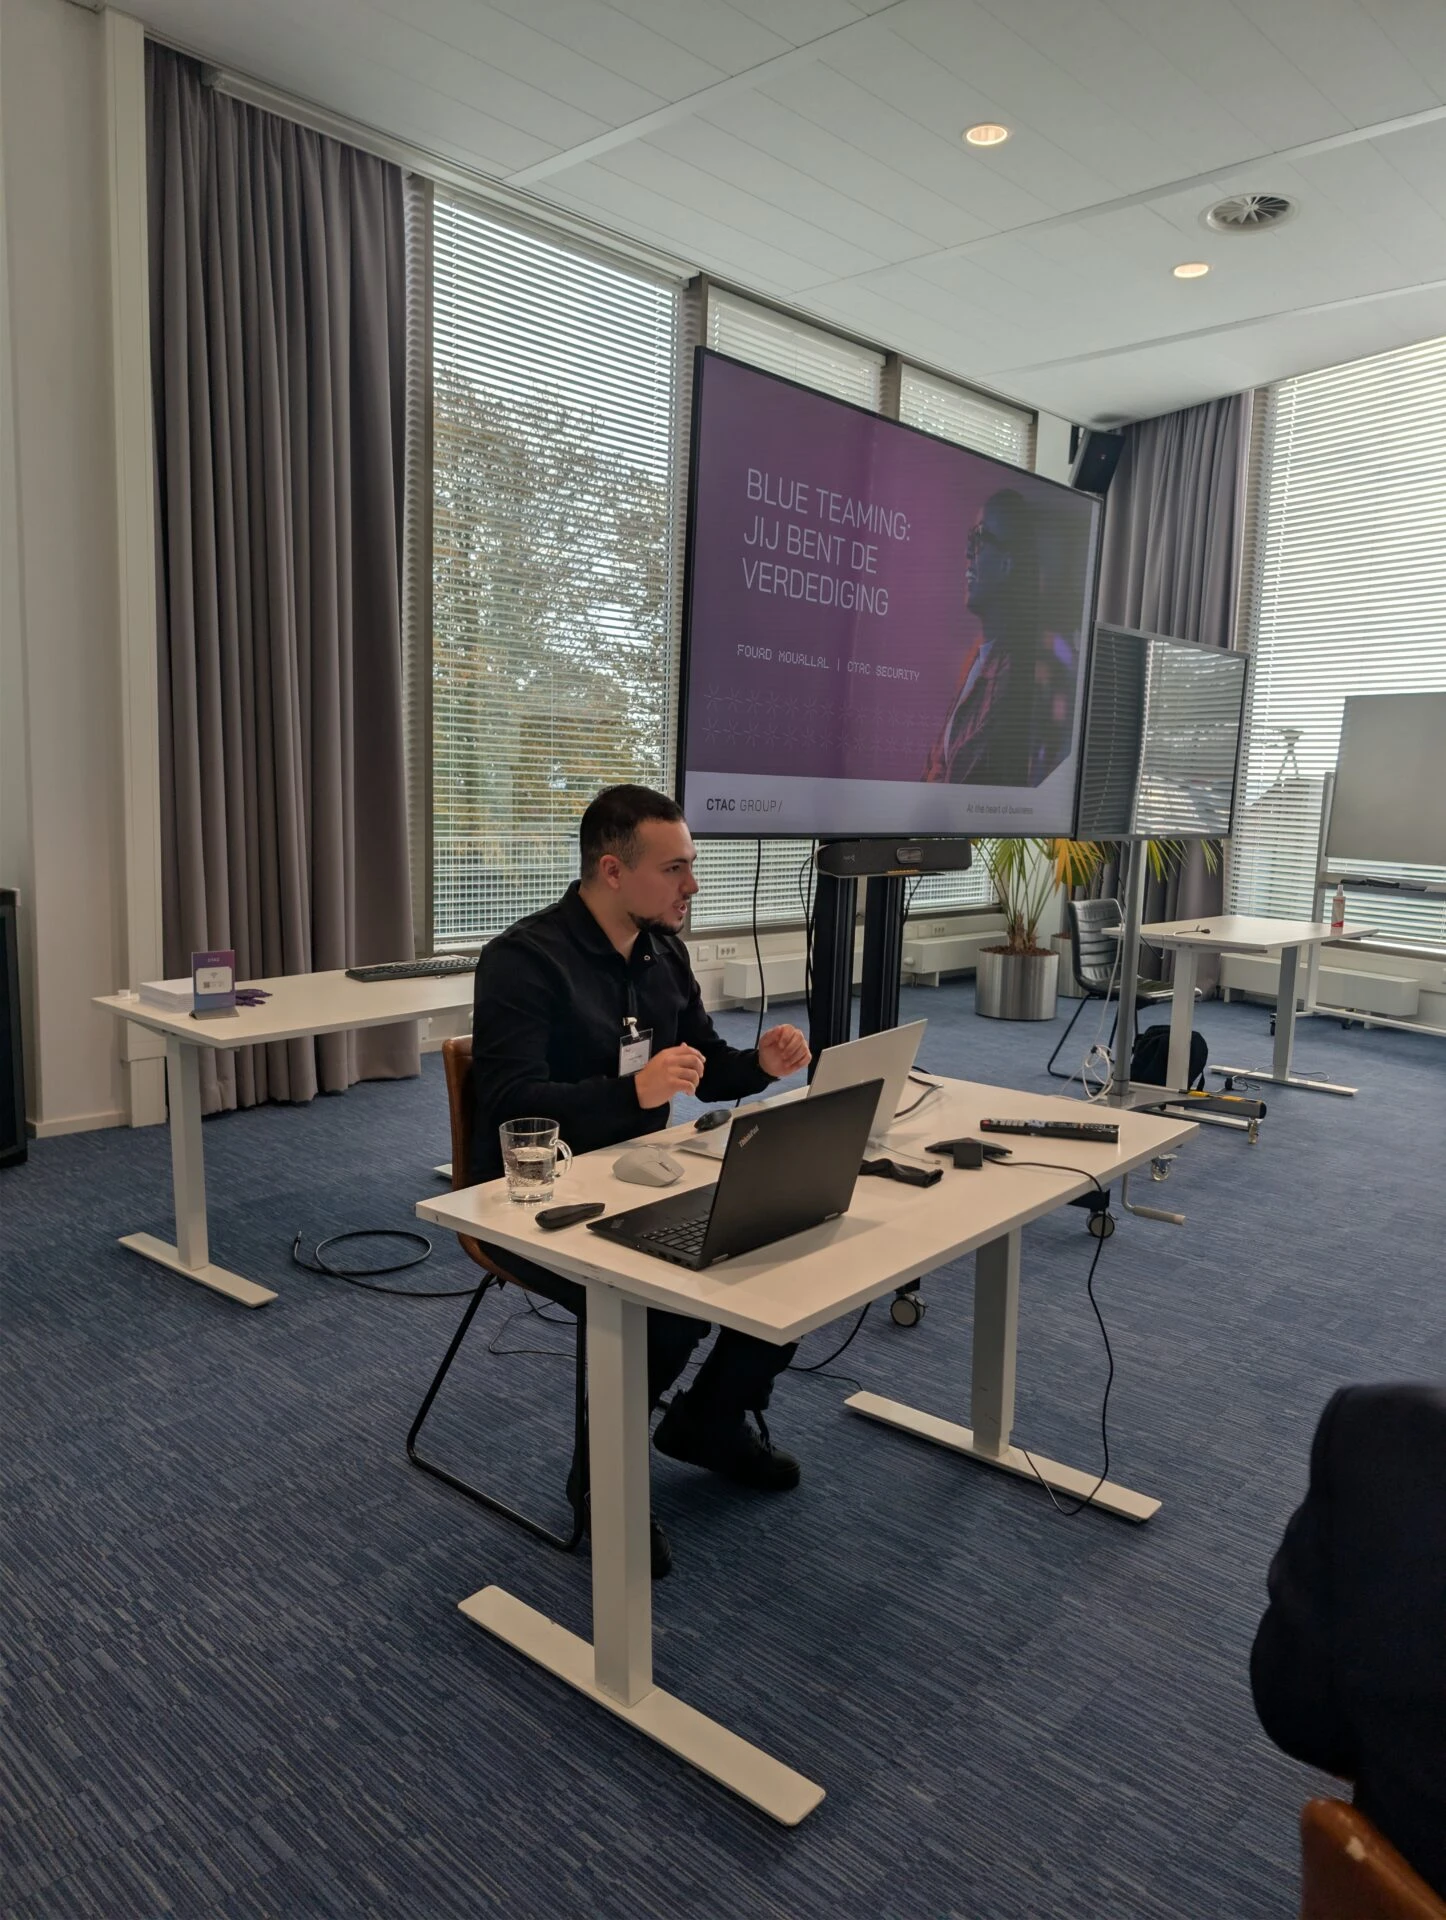
Cybercriminals are becoming more professional, attacks smarter and the potential impact greater. Yet the deciding factor often isn’t the attack itself, but how well an organization is prepared for it. During the Ctac Security Event “Cyberattack under control: from threat to responsibility”, security experts took participants through the full lifecycle of a cyber incident. From the first phishing email and the attacker’s methods to detection by a Security Operations Center (SOC), safe AI use and the responsibility of the board and executive management. The key takeaway of the morning? Cyber resilience doesn’t come from one tool or measure, but from the interplay between technology, people, processes and executive decision-making.
One attack, seen from two perspectives
What does your organization look like through the eyes of an attacker? And what happens when that attacker actually gains access to an account? Anass Ali of Ethical Hacker Groep Nederland showed how cybercriminals combine information from different sources. Public company information, leaked personal data and convincing phishing techniques are often enough together to deceive an employee.
In a live demonstration, participants saw how an attacker uses a fake Microsoft login environment to take over an account and an active session. With that, the attacker tries to gain access to email, files, SharePoint and Teams, and then spread through the organization from that single account. Above all, the demonstration showed how credible modern phishing is. A familiar corporate identity, a recognizable login screen and a normal MFA prompt don’t guarantee that an environment is safe. Awareness remains important, but it needs technical support, such as properly configured conditional access and phishing-resistant authentication with passkeys, FIDO keys or Windows Hello for Business.